Approved execution boundary
A work package defining authorised personnel, access conditions, permitted tools and material-handling requirements, grounded in the customer's instructions for the specific environment and deployment scope.
Build within the boundaries your environment requires
Sovereign and isolated environments require the delivery method to respect the customer's authority over access, information and support. O-Connect plans field execution around those defined boundaries, including the tools, records and materials permitted on site. Each work package makes dependencies and responsibility visible without assuming that ordinary remote support or information exchange is available.
Preparation establishes who may enter the environment, what they may bring and how work can be authorised. We confirm the approved procedures for equipment receipt, software or configuration transfer, documentation and removal of materials. Where connectivity is restricted, the plan accounts for the customer-approved means of receiving instructions, collecting evidence and obtaining engineering decisions during execution.
Support boundaries need the same attention as the initial installation. We identify the permitted escalation route, the information that may be shared and the authority required for any transfer beyond the environment. Records are prepared for the customer's approved custody and review process. The customer defines its sovereignty, security and jurisdiction-specific requirements and remains responsible for assessing them.
A work package defining authorised personnel, access conditions, permitted tools and material-handling requirements, grounded in the customer's instructions for the specific environment and deployment scope.
A record of the approved methods and owners for transferring required configurations, instructions and evidence, including how restricted connectivity affects deployment preparation and engineering support.
Asset, connection and validation records prepared through the permitted capture process, with custody and access aligned to the customer's stated requirements for project documentation handling.
A handover defining the authorised support route, escalation contacts and information-sharing limits, so operational teams understand the approvals needed for subsequent assistance within the environment.
Translate customer access and information-handling requirements into an executable field plan, confirming the people, tools, records and materials approved for use before the deployment begins.
Carry out the approved installation and checks through the site's authorization process, recording exceptions and requesting decisions through the designated channel when unexpected dependencies are encountered.
Deliver the permitted evidence into the customer's approved custody, confirm acceptance ownership and review the support boundaries that apply once the installation work has been completed.
The environment is handed over with a clear record of the authorised work, its acceptance evidence and the limits that govern further support. Customer teams retain control of access and information, with deployment dependencies and future escalation responsibilities documented in a form their operating model permits.
Define your acceptance criteriaYes, subject to the approved scope and available customer procedures. We identify which deployment steps depend on external connectivity and agree permitted alternatives with the responsible owners. Required instructions, tools and transfer arrangements must be ready before the affected work is released.
The customer and its appointed advisers define those requirements, including any restrictions on personnel, access, information and support. We translate the agreed requirements into the fieldwork plan. Deployment evidence supports their assessment and does not independently establish legal or policy compliance.
The handover records the customer-approved support route and information-sharing boundaries. Any remote access, evidence transfer or supplier escalation depends on those permissions. Support arrangements are agreed for the specific environment so subsequent assistance follows the same authority model as the deployment.
Coordinate infrastructure deployment with controlled access, segregated network paths and traceable records aligned to your approved site requirements.
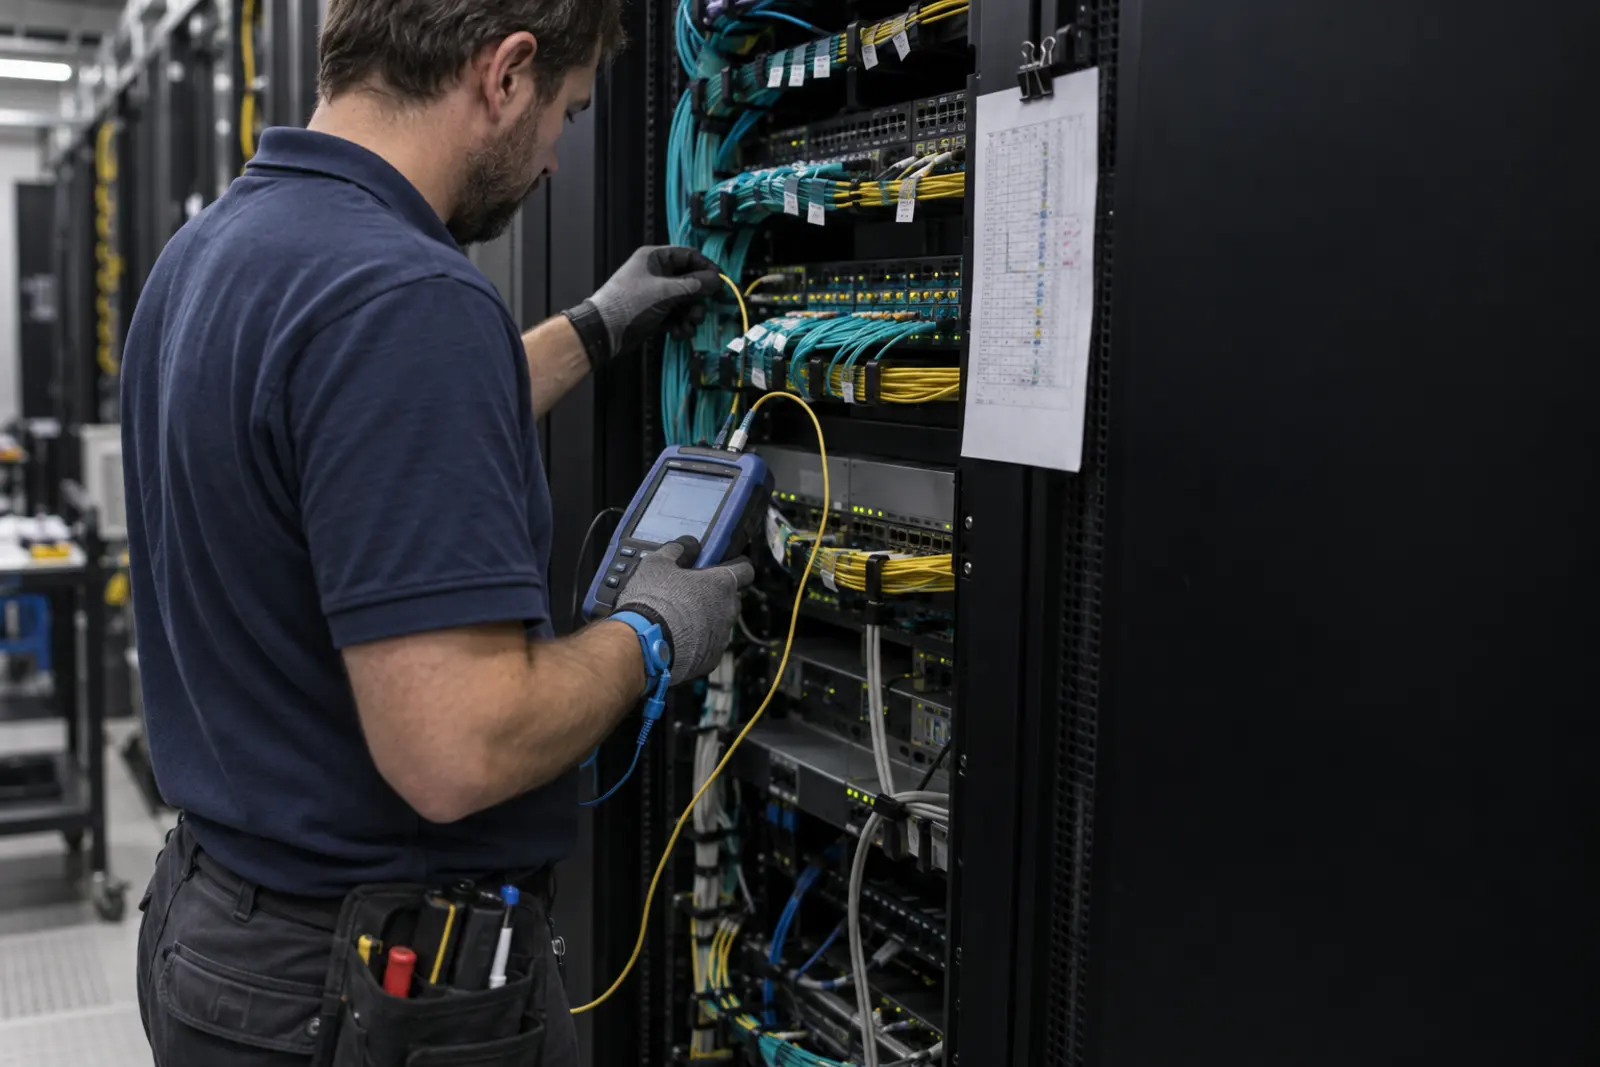
Build an evidence-based handover with agreed checks for firmware, hardware health, thermal behaviour and workloads across the deployed infrastructure.
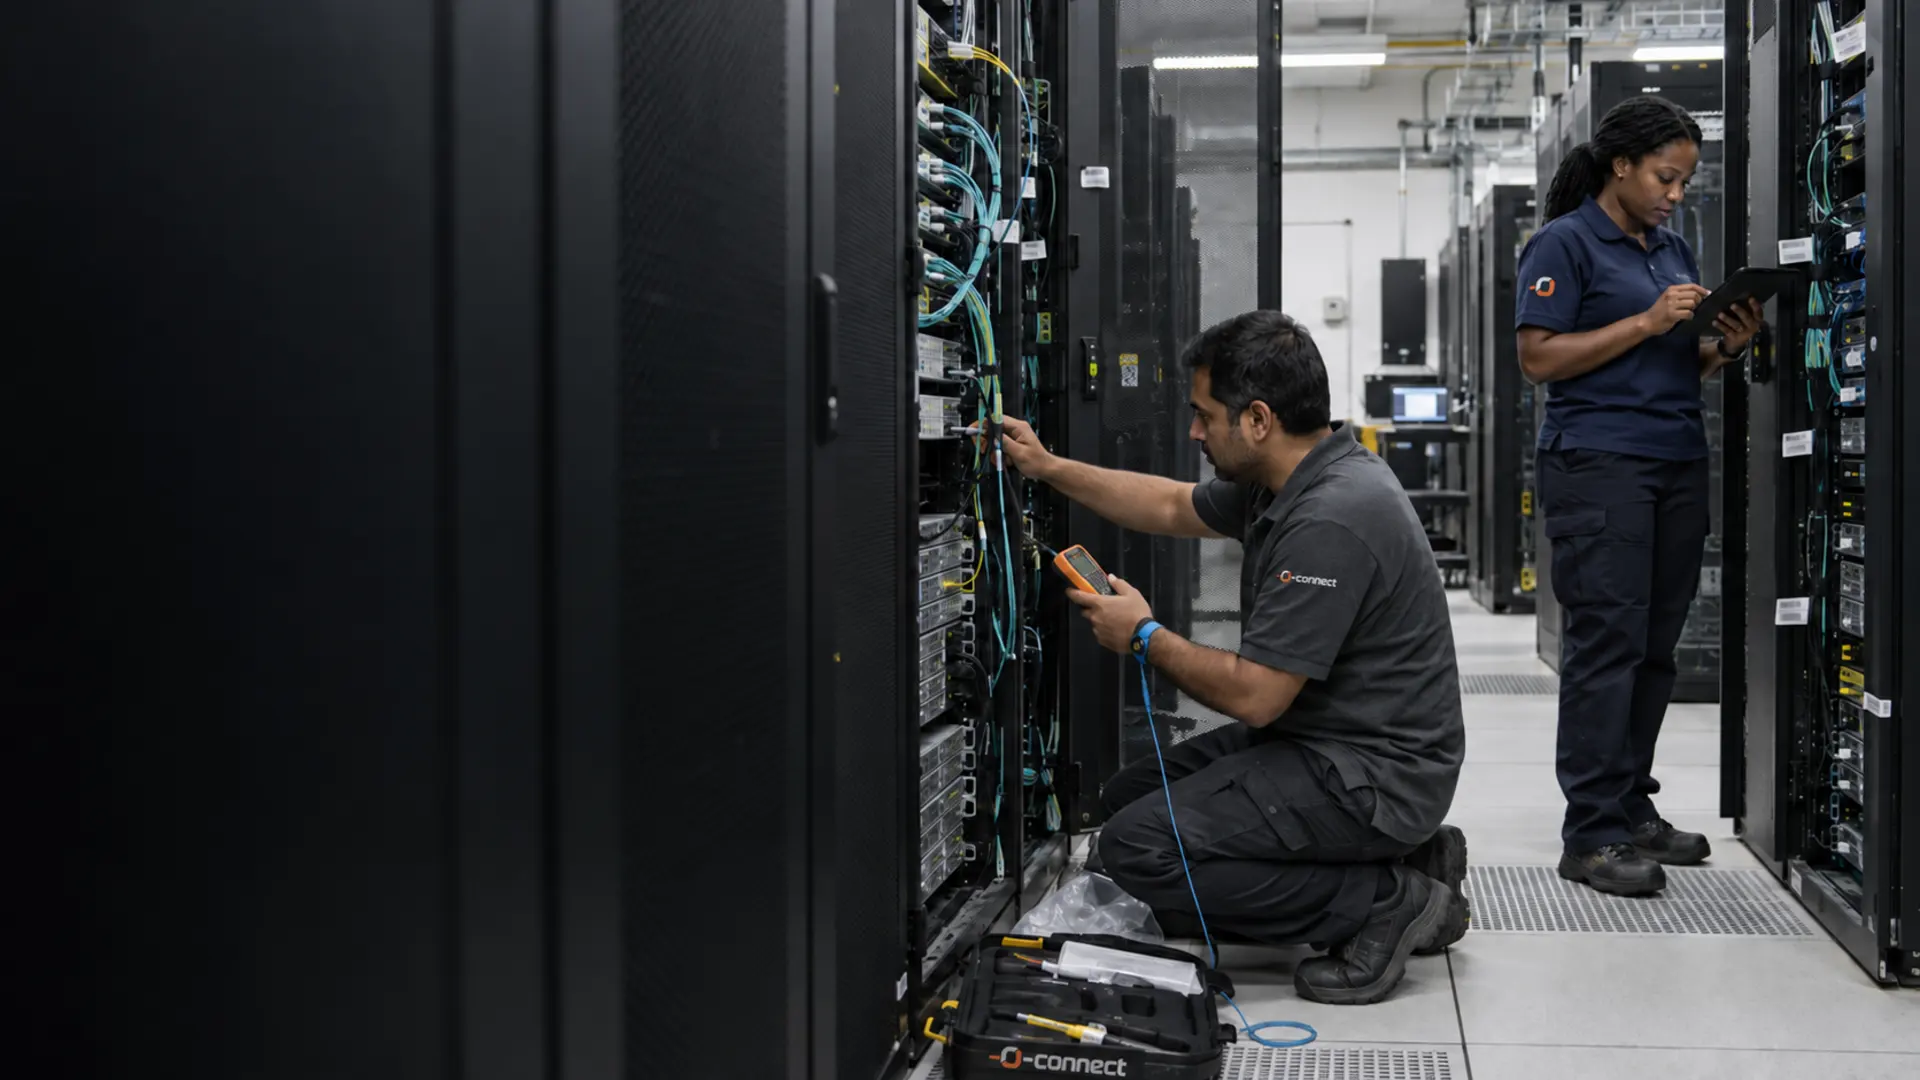
Coordinate field work across infrastructure support, capacity expansion, refresh and decommissioning, with controlled changes and current asset records.